How to verify an Open Badges 3.0 credential
Check an Open Badges 3.0 credential with an independent verifier, inspect its data, and understand what a successful result proves.
To verify an Open Badges 3.0 credential, check its structure, digital signature, validity dates, and revocation status. Then confirm that you trust the issuer and that the credential belongs to the person presenting it.
If you evaluate credentials for a university, start with one credential you can inspect outside the issuing platform.
Get the credential file
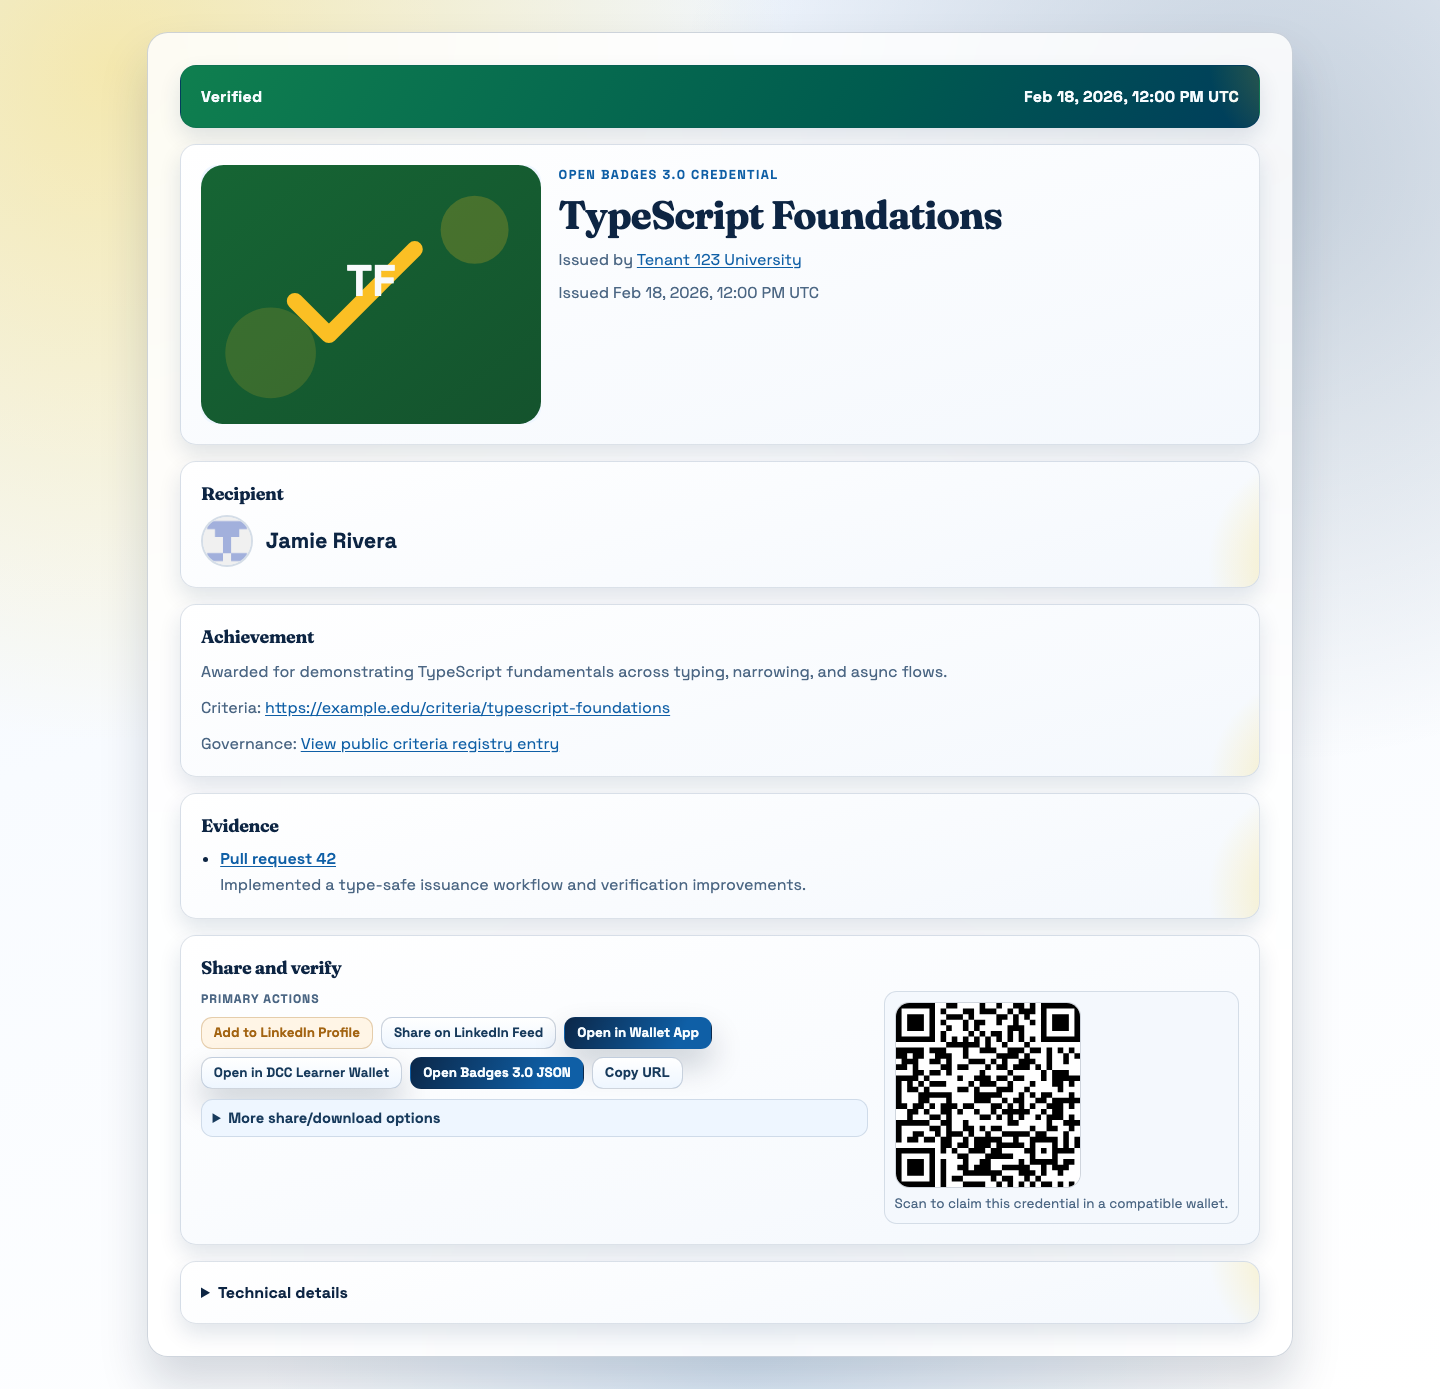
Ask for the signed credential file or its download URL. A screenshot of a badge does not contain the data you need to check its signature.
For a JSON credential, save the file as credential.json. With jq, you can inspect a few useful fields:
jq '{
  issuer: .issuer,
  achievement: .credentialSubject.achievement.name,
  recipient: (.credentialSubject.id // .credentialSubject.identifier),
  proof: .proof,
  status: .credentialStatus
}' credential.json
This command displays data; it does not verify the signature. Some credentials use a JSON Web Token (JWT), which needs a verifier that supports that format. The Open Badges specification describes the verification requirements for both formats.
Run an independent verifier
Open the 1EdTech Open Badges 3.0 verifier. Upload the credential or provide its URL, then submit it. Use a public example or a credential you have permission to share with the service.
Read the report and download a copy. Check the individual results:
- Does the credential conform to the expected structure?
- Does its signature verify with a key authorized by the issuer?
- Is it within its validity period?
- If it declares a status mechanism, does that check succeed?
These checks follow the Open Badges verification process. If a key or status service cannot be reached, treat that part of the result as unresolved. A missing status field does not establish that the credential can never be revoked.
For the signing side, see how CredTrail signs Open Badges 3.0 credentials.
Check the issuer and recipient
A successful signature check establishes who signed the credential and whether its signed content has changed. You still need to decide whether that issuer is qualified to make the claim. The W3C credential trust model leaves that decision to the verifier.
Confirm the issuer through a source you already trust, such as the university’s official website. Match the recipient identifier through your institution’s identity process. A person’s possession of a credential file alone does not establish that it was issued to them.
For an institutional review, use the Open Badges governance guide to assign responsibility for issuer keys, revocation, and ongoing verification.